Start with the exact purpose of the session
Before a customer joins the video call, the purpose of the session must be plain. The agent needs to know whether the check is for onboarding, account opening, a refresh review, or an exception case that needs closer handling. That purpose shapes the script, the questions asked, the records kept and the people allowed to see the file.
Keep the intake note specific. A vague request such as identity check is too loose for a team that must later explain what was collected, why it was collected and who handled it. A clear workflow also helps operations, training and quality control stay on the same page.
- Record the reason for verification before the session starts.
- Limit collection to the documents and steps needed for that purpose.
- Define who may view the recording, still images and notes.
- Keep the script aligned to the stated onboarding process.
Consent should happen before document capture begins
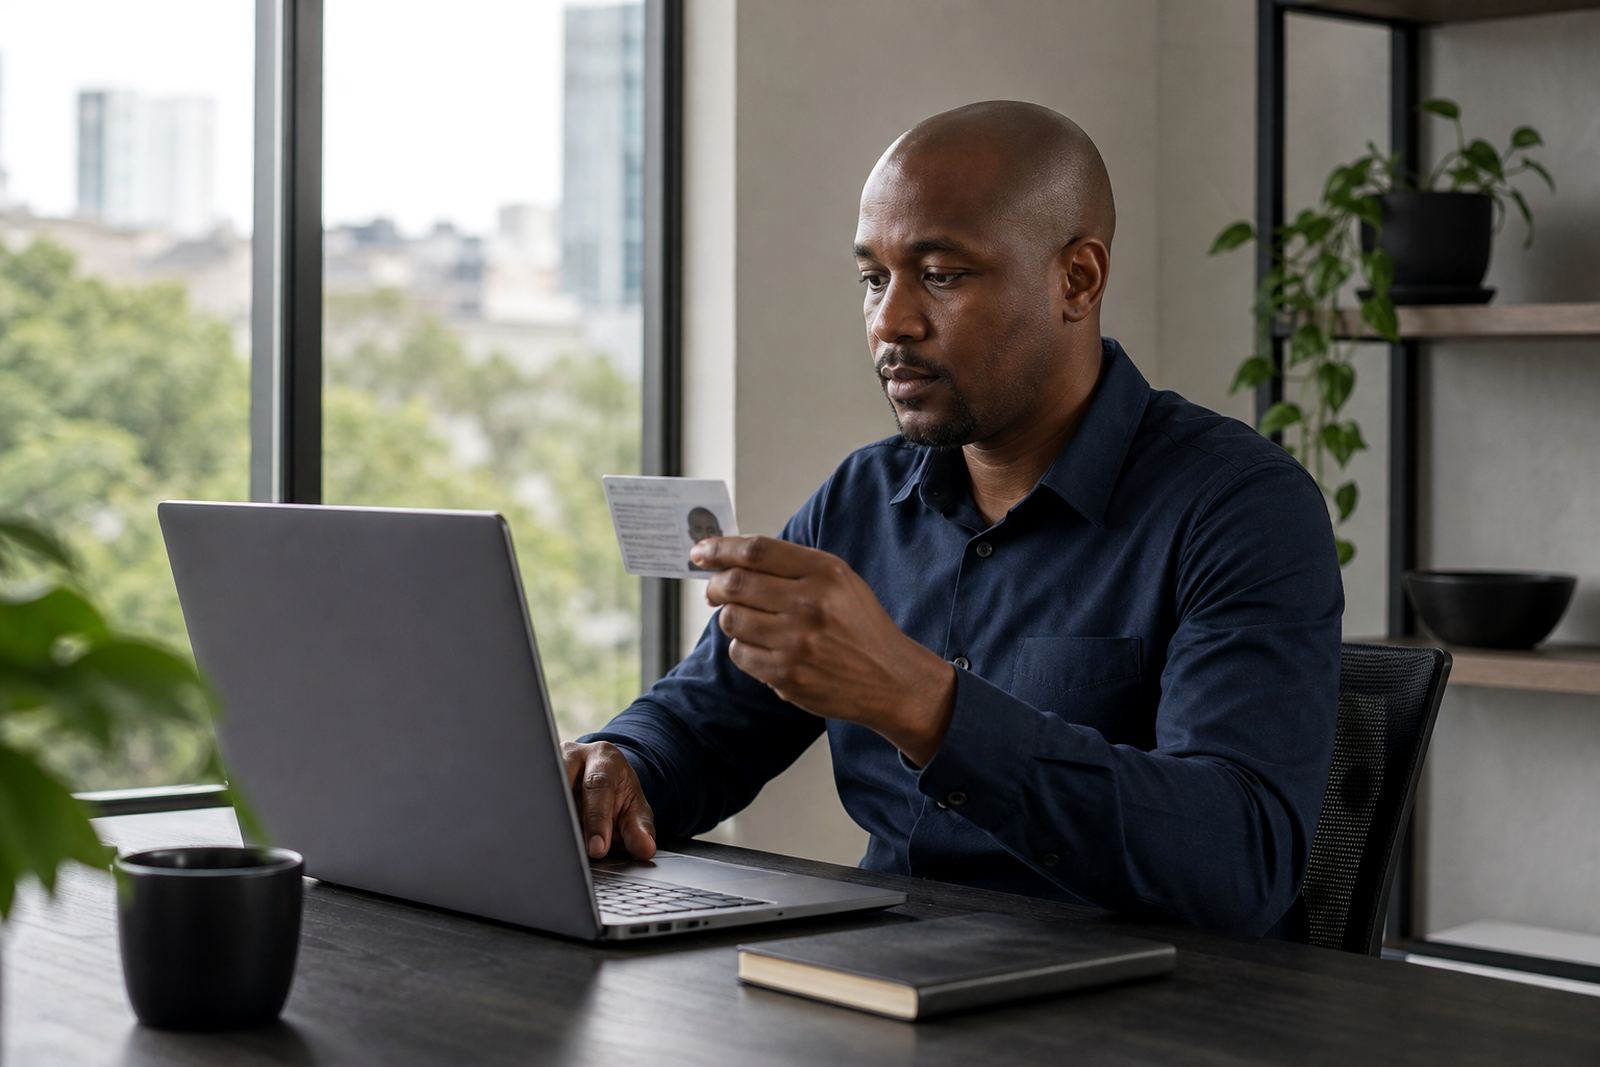
In a guided video session, consent is not a side note. The customer should understand that they are joining a recorded identity check, that an ID document will be shown on camera, and that the session may be used for verification, audit and dispute handling. The agent should ask for clear agreement before any capture starts.
Consent should also cover the way the information is handled after the session ends. If a business stores the video, still frames or metadata, that needs to be stated in the script or in the pre-session notice. The wording should be calm and direct, not crowded with legal language that nobody can follow in the moment.
- Tell the customer the session is recorded, if that is the process.
- Say what will be captured, including the ID document and live face check.
- Explain who may review the record internally.
- Keep a dated note that consent was given in the session.
Handle identity evidence with narrow access
Video KYC produces several record types at once. There may be the live video stream, a saved recording, ID document images, screen notes and the final verification result. Each item should have its own storage rule. Staff do not all need the same access, and the quality team should not be browsing files that have no bearing on their role.
Access control matters most when teams are spread across Johannesburg, Pretoria, Cape Town, Durban and Gqeberha. The business can still keep one process, but the records must be separated by function. Operations may need the session log, while training may only need a redacted example. That separation reduces clutter and lowers the chance of unnecessary viewing.
- Use role based access for recordings and supporting files.
- Keep audit notes separate from the customer profile where possible.
- Redact example material used for training sessions.
- Review who can export, copy or share a record.
Use liveness checks without turning the script into theatre
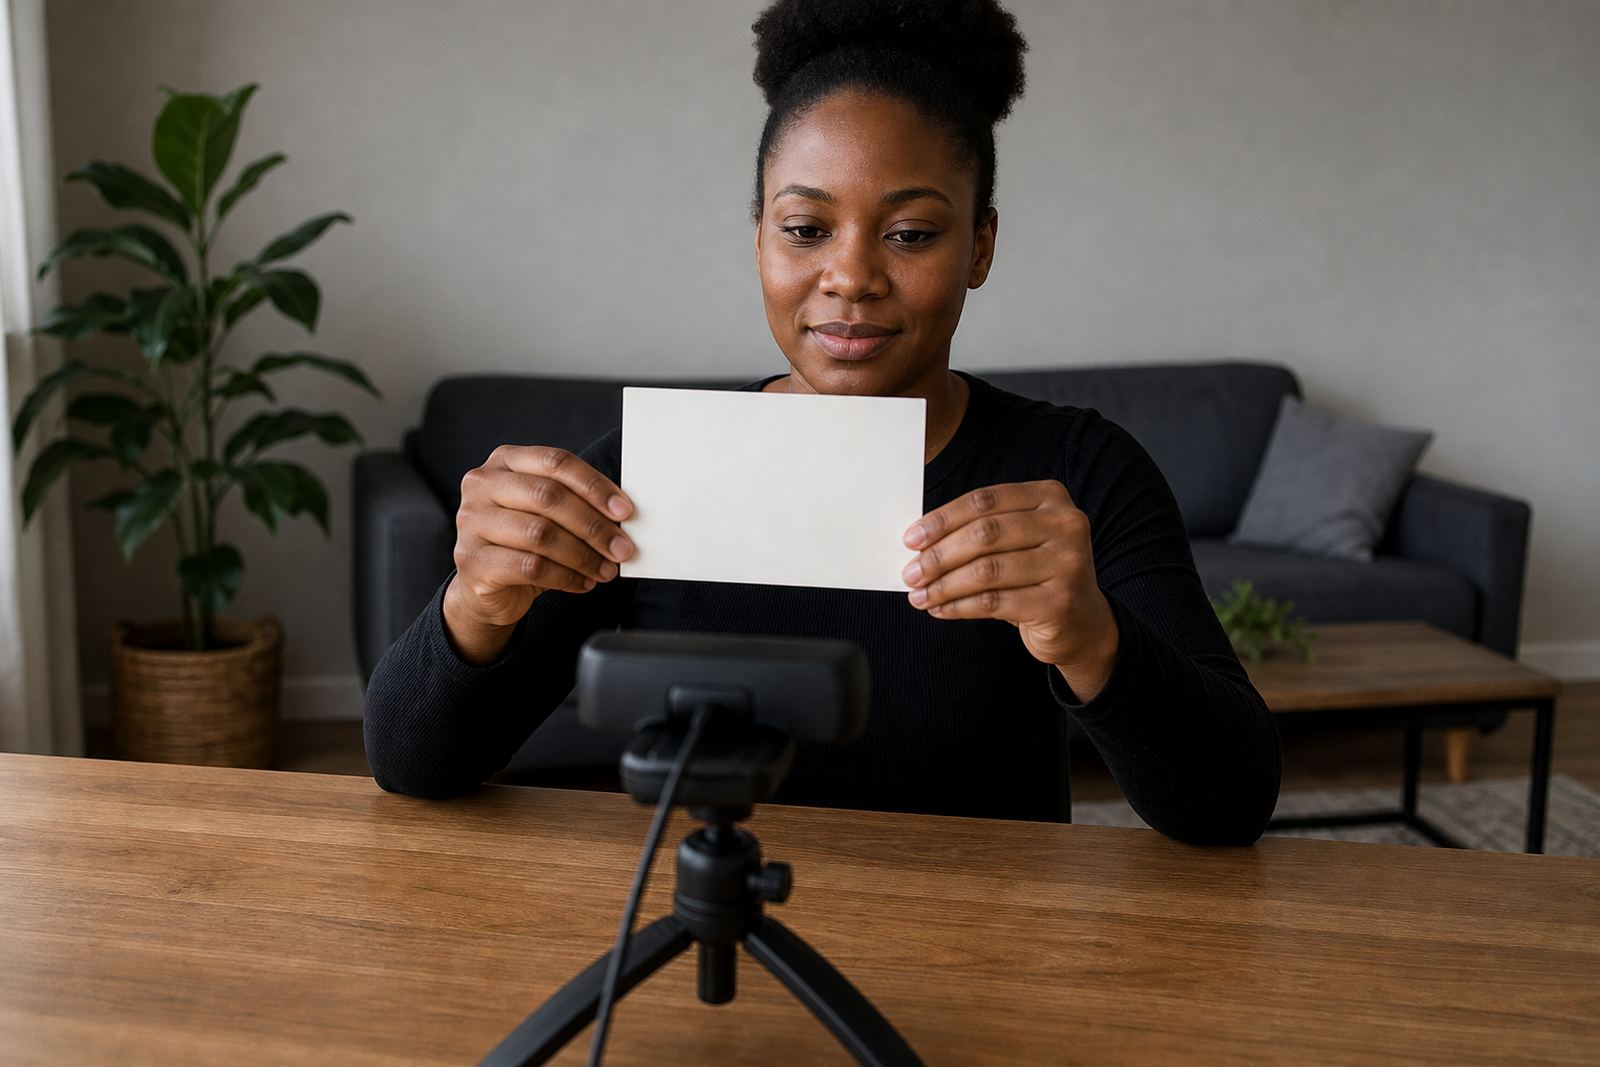
A good identity session checks that a live person is present and that the person on screen matches the document. Simple liveness prompts are better than dramatic ones. Ask the customer to turn their head, blink on request, or adjust the document angle if the image is unclear. The point is to test presence and document integrity, not to make the call feel like a performance.
The agent should keep the language steady and repeat only what is needed. If the ID photo is blurry, say so. If the lighting is poor, ask for a better position. If the document is expired or the picture does not match, note the issue plainly and move to the escalation path. That sort of record keeping protects the business and gives the compliance team a usable trail.
- Check the face match and the document details in the same session.
- Use short liveness prompts that are easy to repeat consistently.
- Log any mismatch, blur or screen glare without softening the note.
- Escalate unclear cases instead of forcing a pass.
Training the team to follow the same privacy habits
Privacy handling is only as tight as the least careful person in the chain. A good training pack should cover the script, acceptable wording, how to pause a session, what to do when consent is not given, and how to save records in the right place. Staff also need to understand what they may not say, especially when a customer asks for informal guidance on how the system works.
For teams in Rosebank, Johannesburg and across the country, refresh training helps keep habits steady when the process changes. Agent script design, escalation design and quality monitoring all support the same goal: fewer loose steps and clearer proof of what happened in each session.
- Train agents on consent wording and document handling.
- Show staff how to pause or end a session when needed.
- Use quality checks to catch weak notes and skipped steps.
- Refresh the script when workflow changes affect privacy handling.
Keep records long enough to serve the process, not longer than needed
Record keeping should follow the business need, not habit. Keep what is needed for verification, internal review and dispute handling, but avoid stockpiling material that has no active purpose. A tidy retention rule makes storage easier to manage and helps staff know when a file is closed.
Where a customer wants their information corrected or reviewed, the team should know how to route that request without improvising. The process should also show how to mark a session as complete, how to archive the outcome, and how to control any later access to the file. That discipline is useful for FICA related due diligence in general terms, and for privacy aware handling under POPIA.
- Set a retention rule for videos, stills and notes.
- Archive completed files in a controlled location.
- Track later access to closed records.
- Use a simple internal route for corrections or disputes.
A practical handover for integration and operations teams
When a business connects the verification flow into its own systems, privacy must be built into the handover. Integration planning should show where data enters, where it is stored, who sees it and what happens if the session fails. API coordination matters here, because a clean technical link should not create a messy privacy trail.
Operational reporting should help the client see patterns without exposing more data than needed. If a workflow needs change request support, the privacy notes should be updated at the same time, not later. Pilot launch support and go live stabilising are useful moments to check whether the script, storage rules and escalation design still match the intended process.
- Map every data handoff before the workflow goes live.
- Check that systems only store what the process needs.
- Review reports for unnecessary personal detail.
- Update scripts and controls when the workflow changes.